> For the complete documentation index, see [llms.txt](https://docs.decube.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.decube.io/business-intelligence/powerbi.md).
# PowerBI
Add a PowerBI connection to your decube so that you can discover the lineage of your assets from source to dashboards.
## Supported Capabilities
{% tabs %}
{% tab title="Supported Capabilities" %}
**General**
* **Metadata** — metadata extraction and display of asset information (tables, columns, schemas). Types collected: Schema, Virtual Table, Virtual Column, Chart, Dashboard
* **Configurable Collection** — selective ingestion of schemas/workspaces in Data Source Management
{% endtab %}
{% tab title="Not Supported" %}
**General**
* Profiling
* Preview
* Data Quality
* External Table
* View Table
* Stored Procedure
{% endtab %}
{% endtabs %}
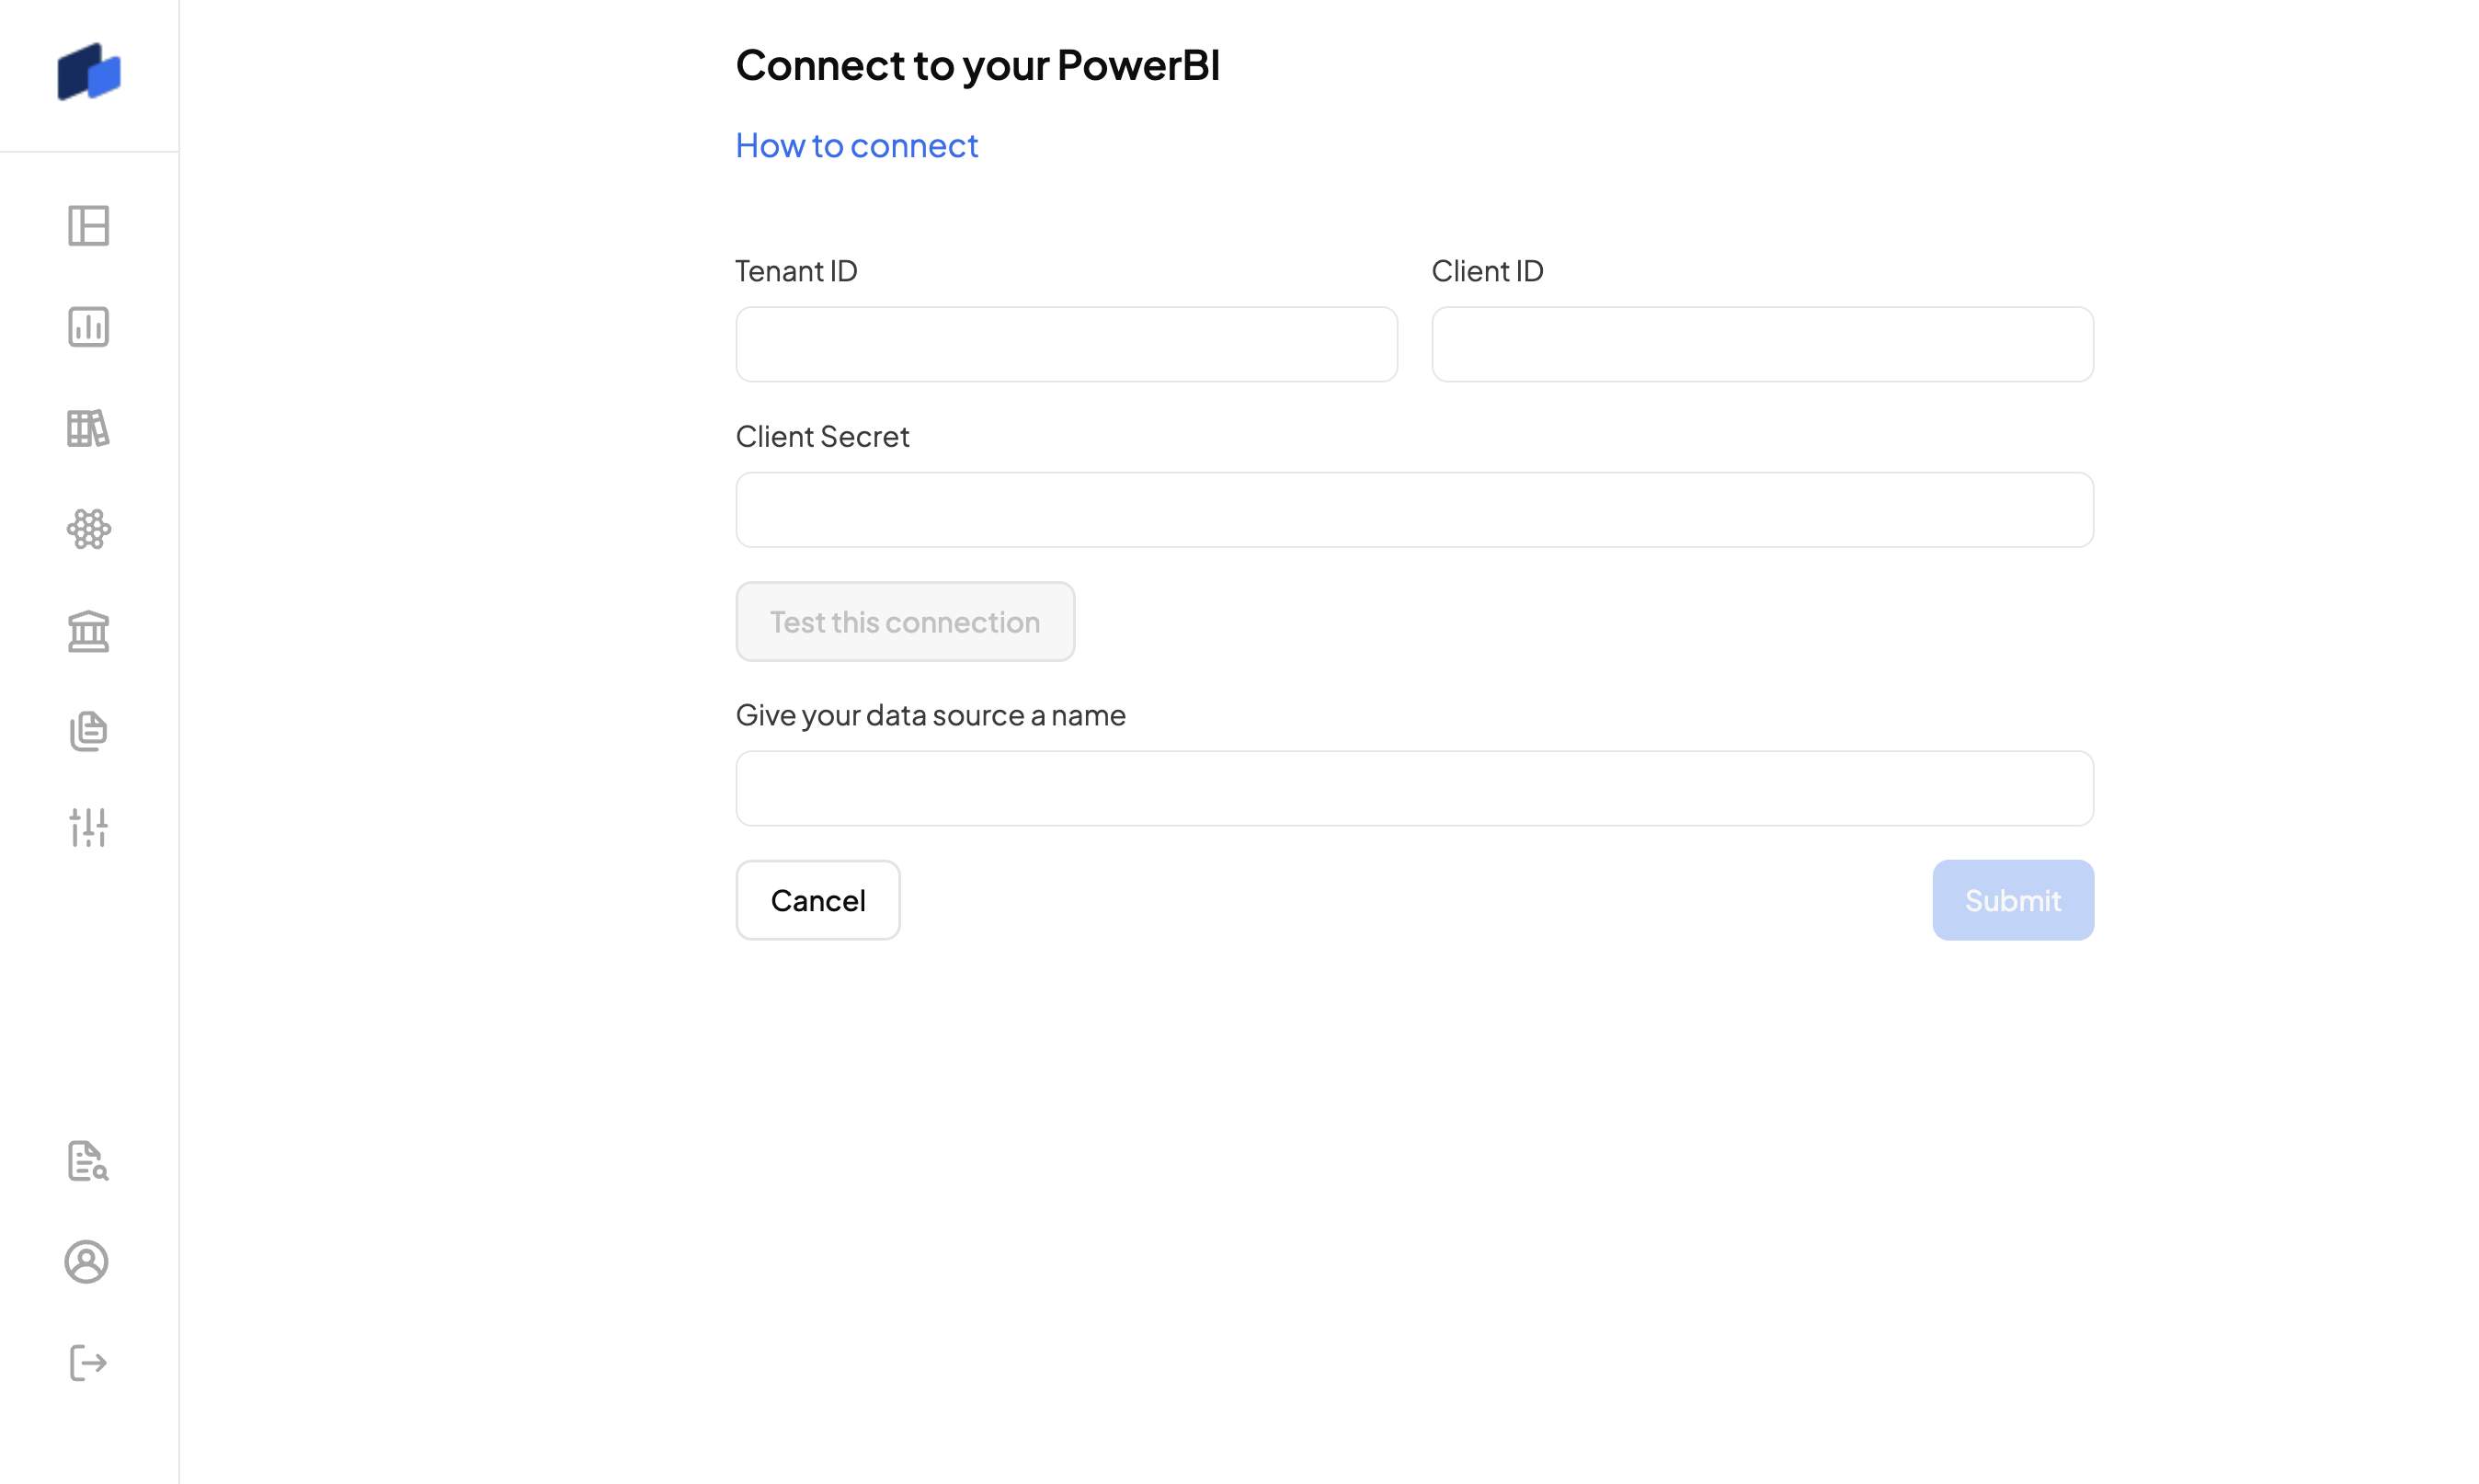
Connecting to PowerBI requires credentials that can be configured and found through this guide. These credentials include:
* `Tenant ID`
* `Client ID`
* `Client Secret`
PowerBI
To note, for complete Lineage to report sources, with [additional configurations](/transformation-tools/additional-configurations.md) we only support sources from:
* BigQuery
* PostgreSQL
* Microsoft SQL
* Snowflake
* Synapse
{% hint style="warning" %}
**The connector might be rate-limited when it is scanning more than 1000 workspaces.**
{% endhint %}
### Prerequisite
1. Access to Azure Active Directory for service principals.
2. A PowerBI Pro or Premium (Premium per-user or Premium capacity ) workspace.
3. Admin access to PowerBI to change Tenant Settings.
### Creating Service Principals and Security Group
1. Go to Azure Active Directory, under the Manage tab to the left of the screen, look for `App Registrations` and click it.
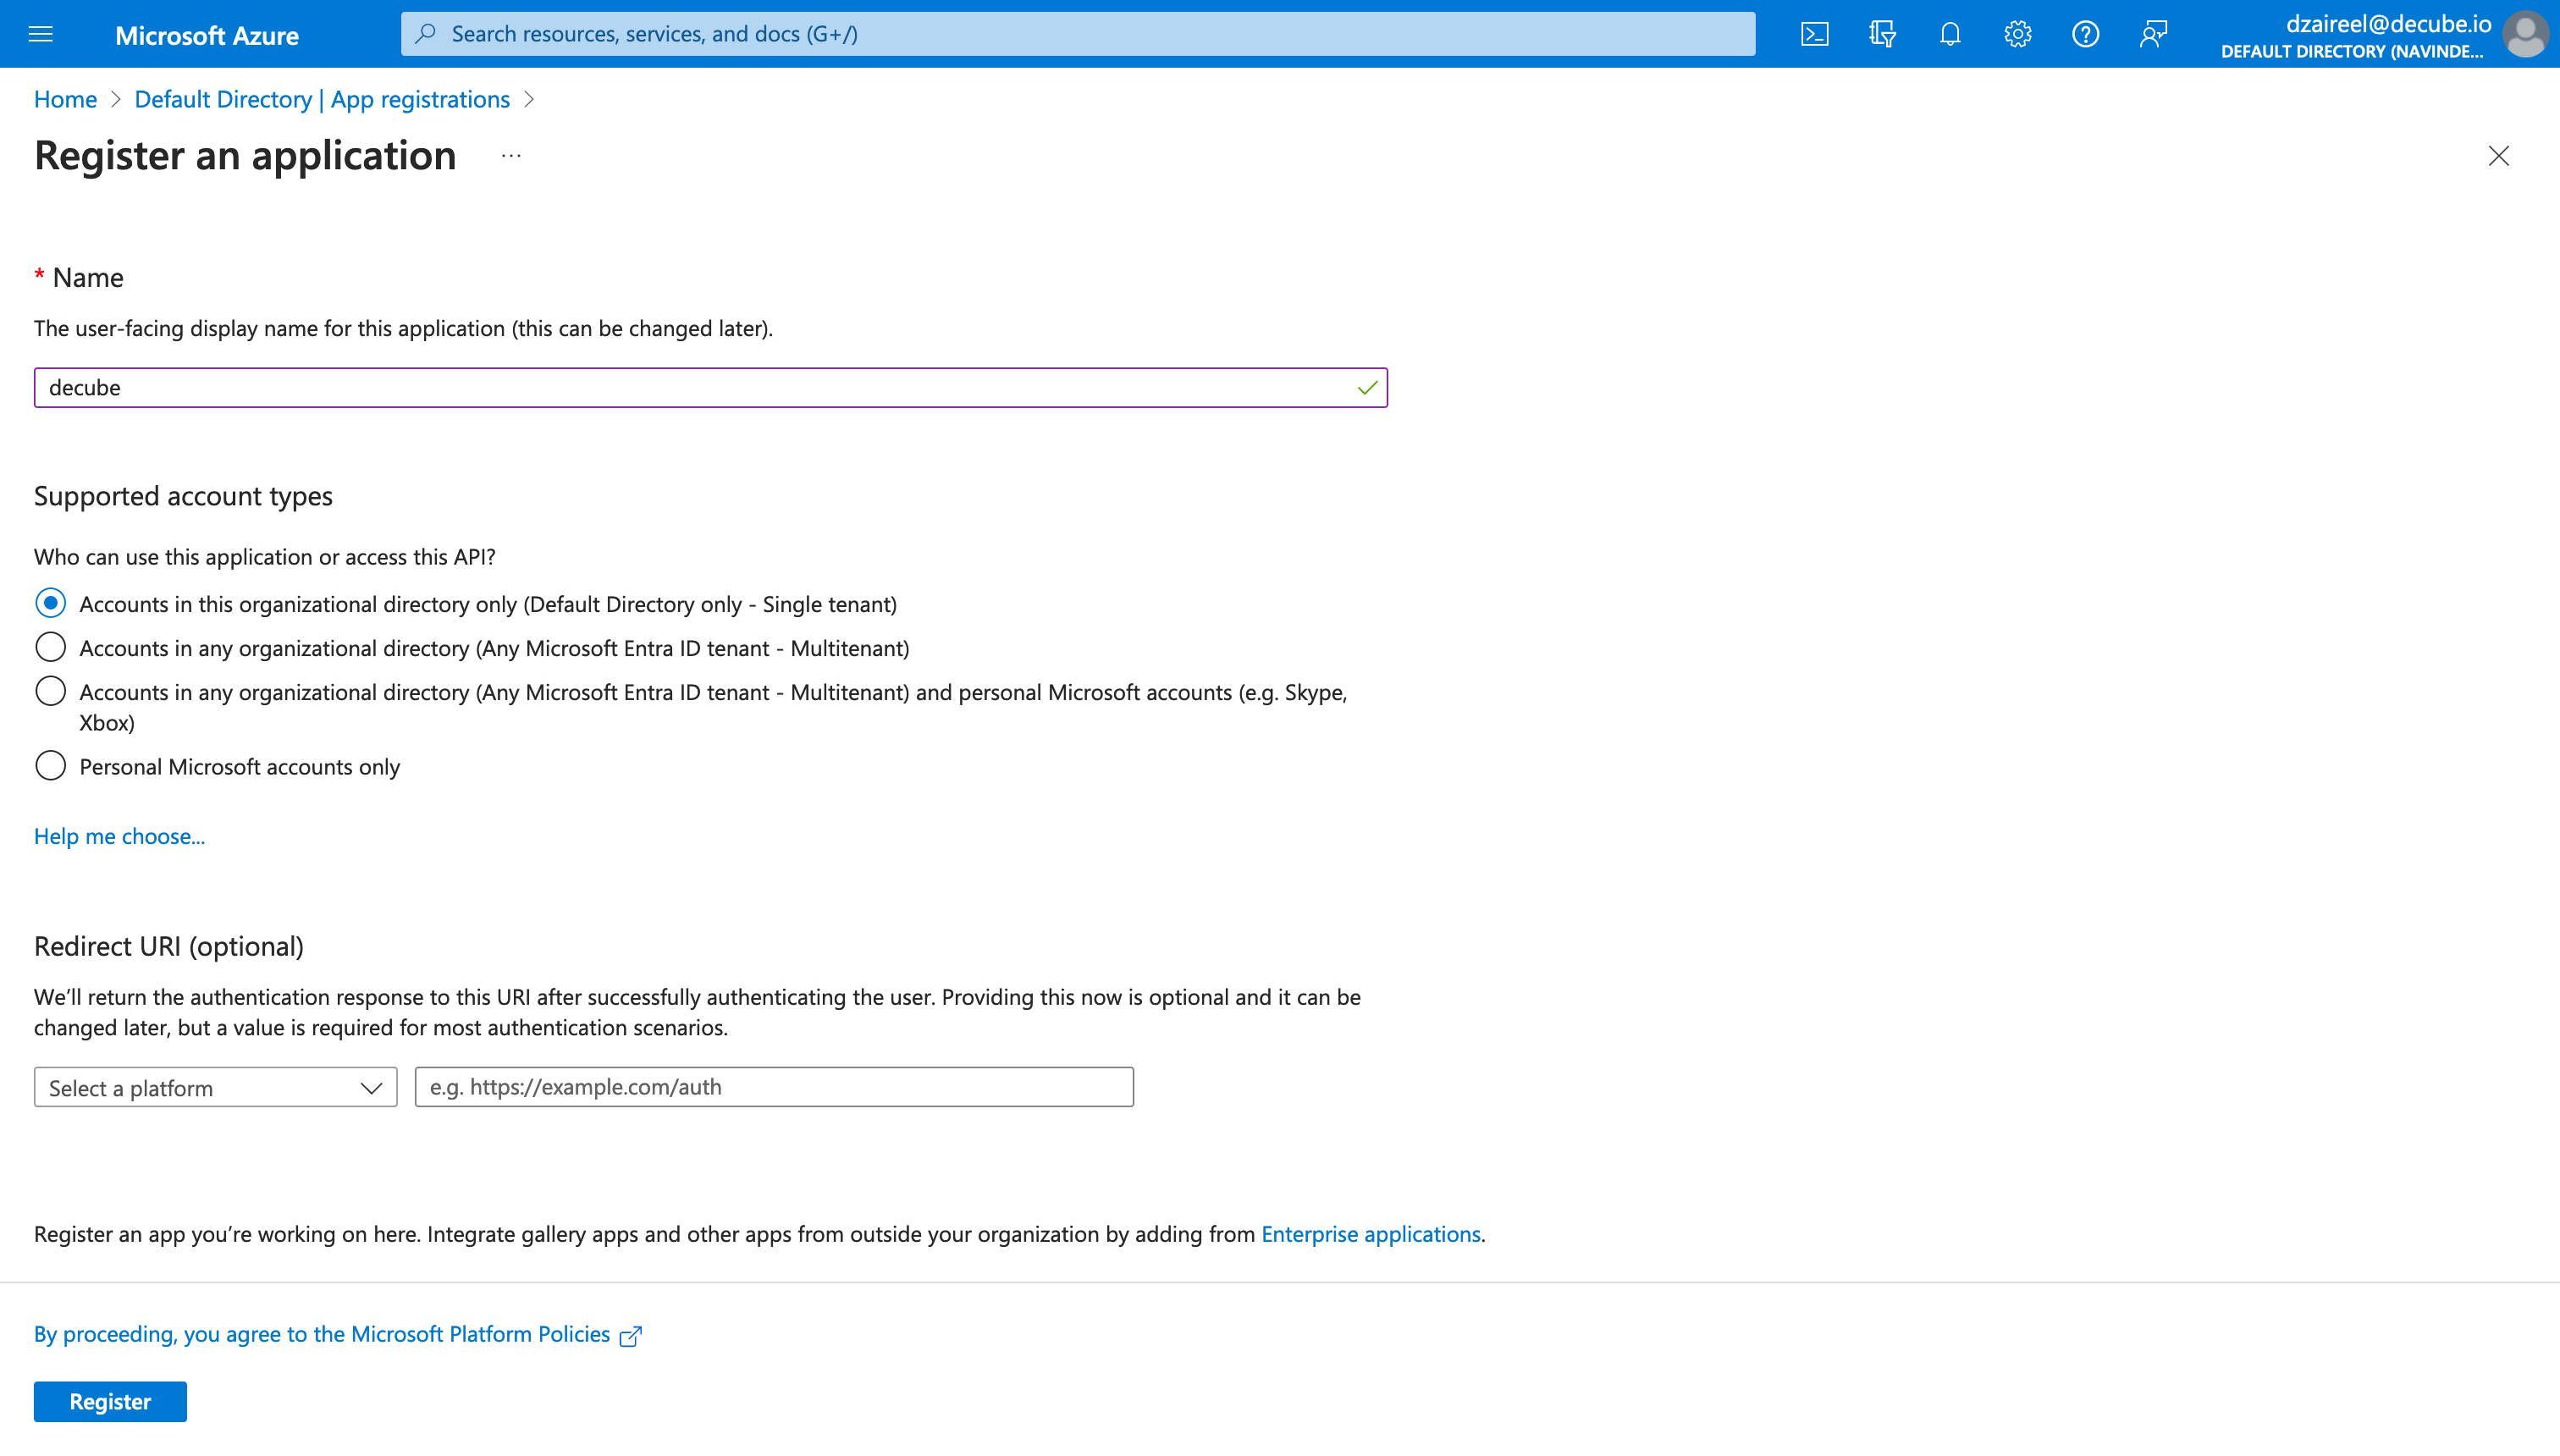
2. Click on `New Registrations` on the top of the tab and you'll be presented with the screen below.
3. We recommend entering `decube` as the Name. Click Register when you are done.
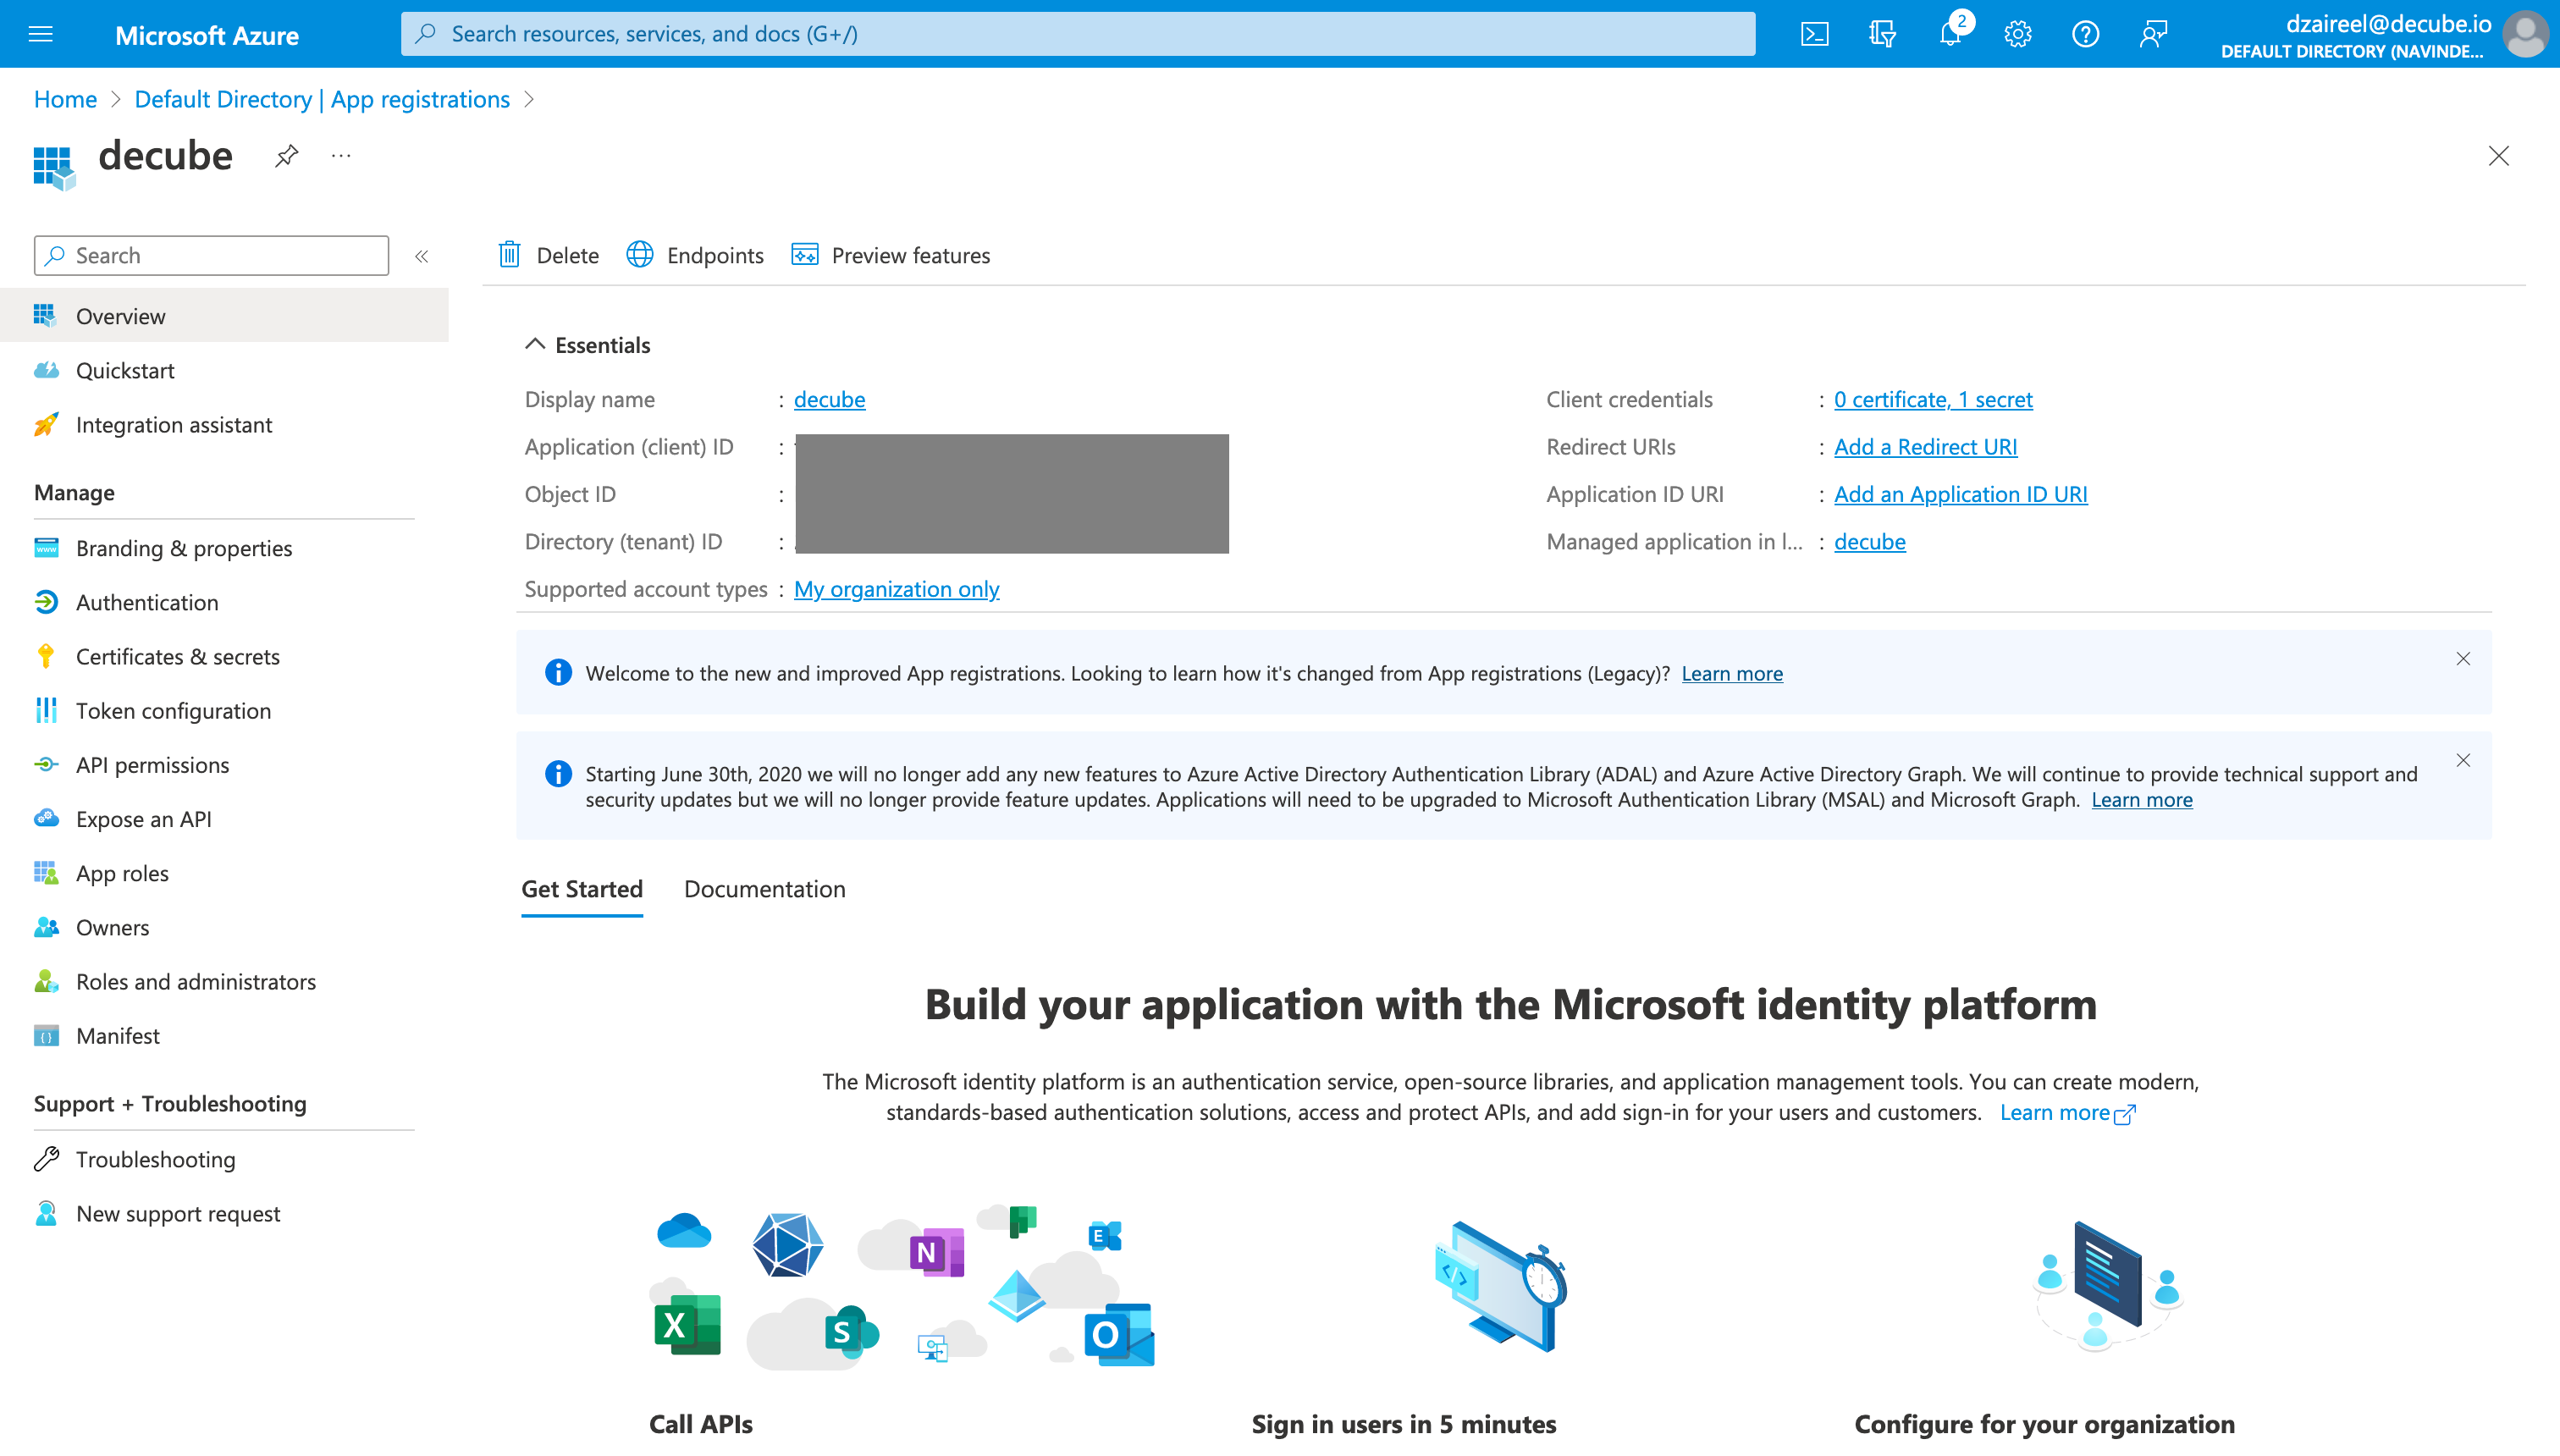
4. Click Overview on the left tab and take note of the `Client ID` and `Tenant ID` we would require when setting up decube.
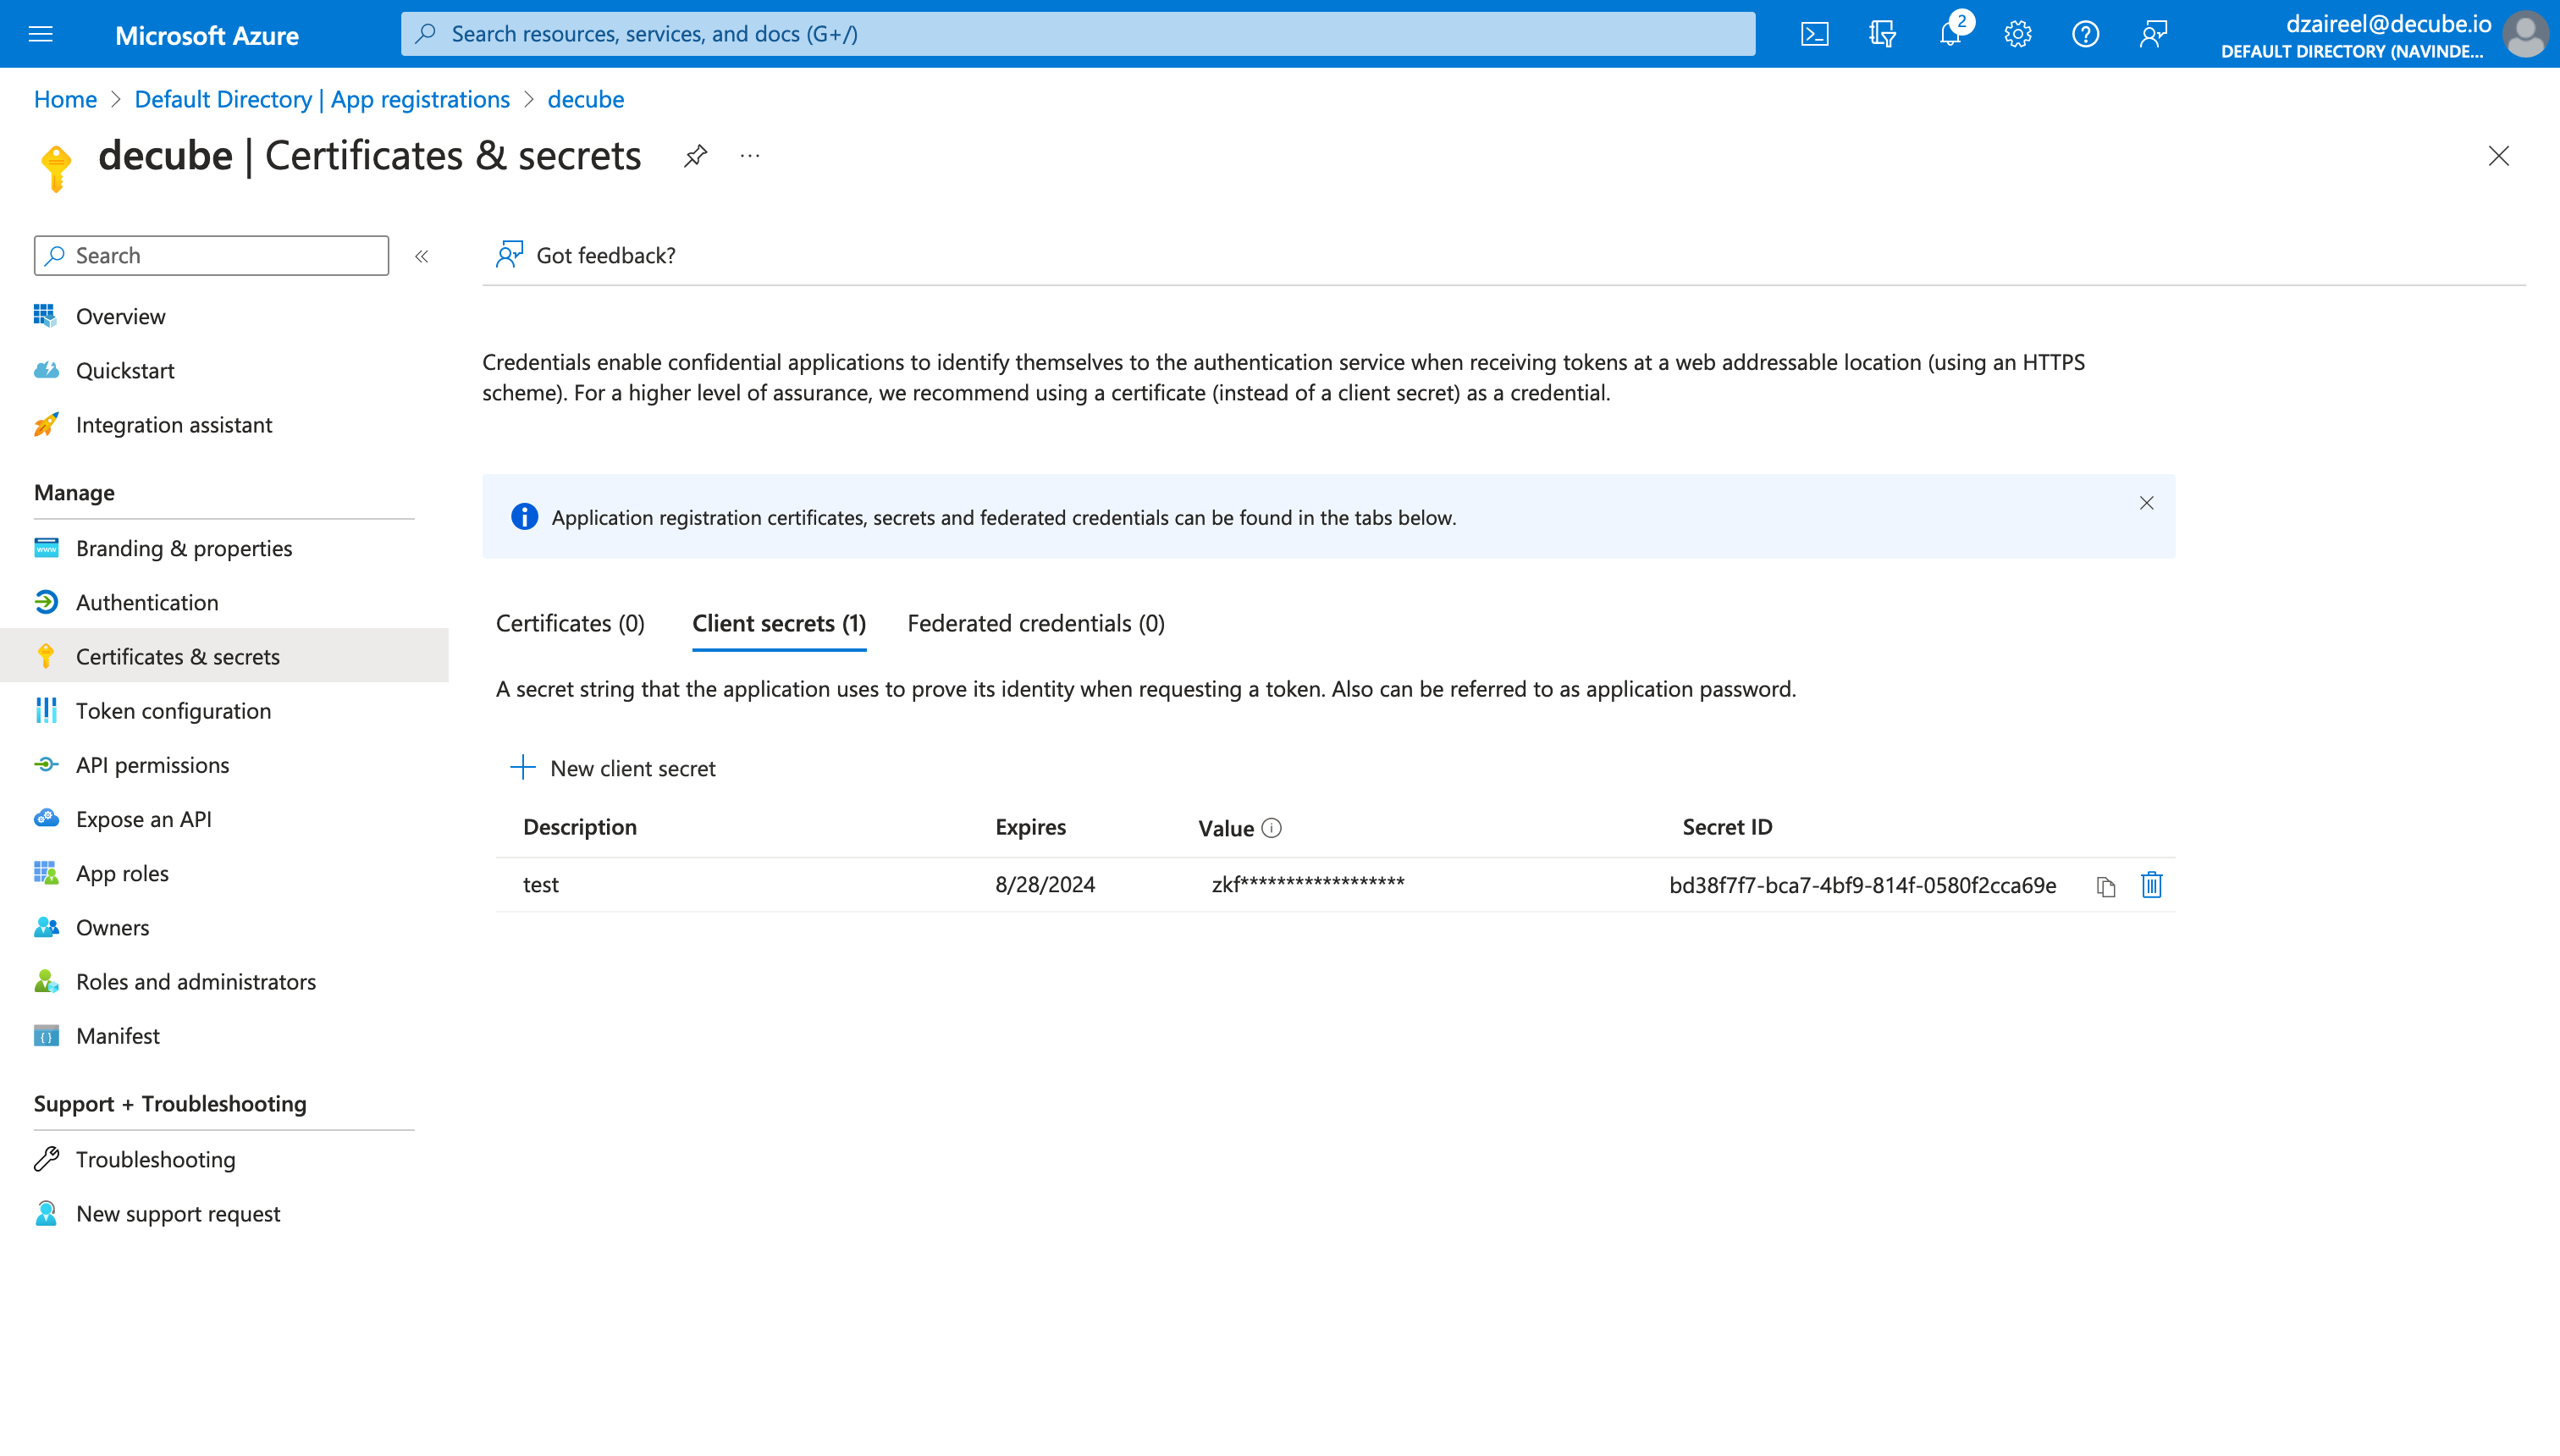
5. Click on `Certificates and Secret`s on the left tab again and click on `New Client Secret` as below. We recommend the description to be `'decube client secret`' and the expiry date to be until the end of your contract with us.
**Make sure to copy the Value of the Client Secret and store it somewhere safe like Azure Key Vault. We will need this value for registration.**
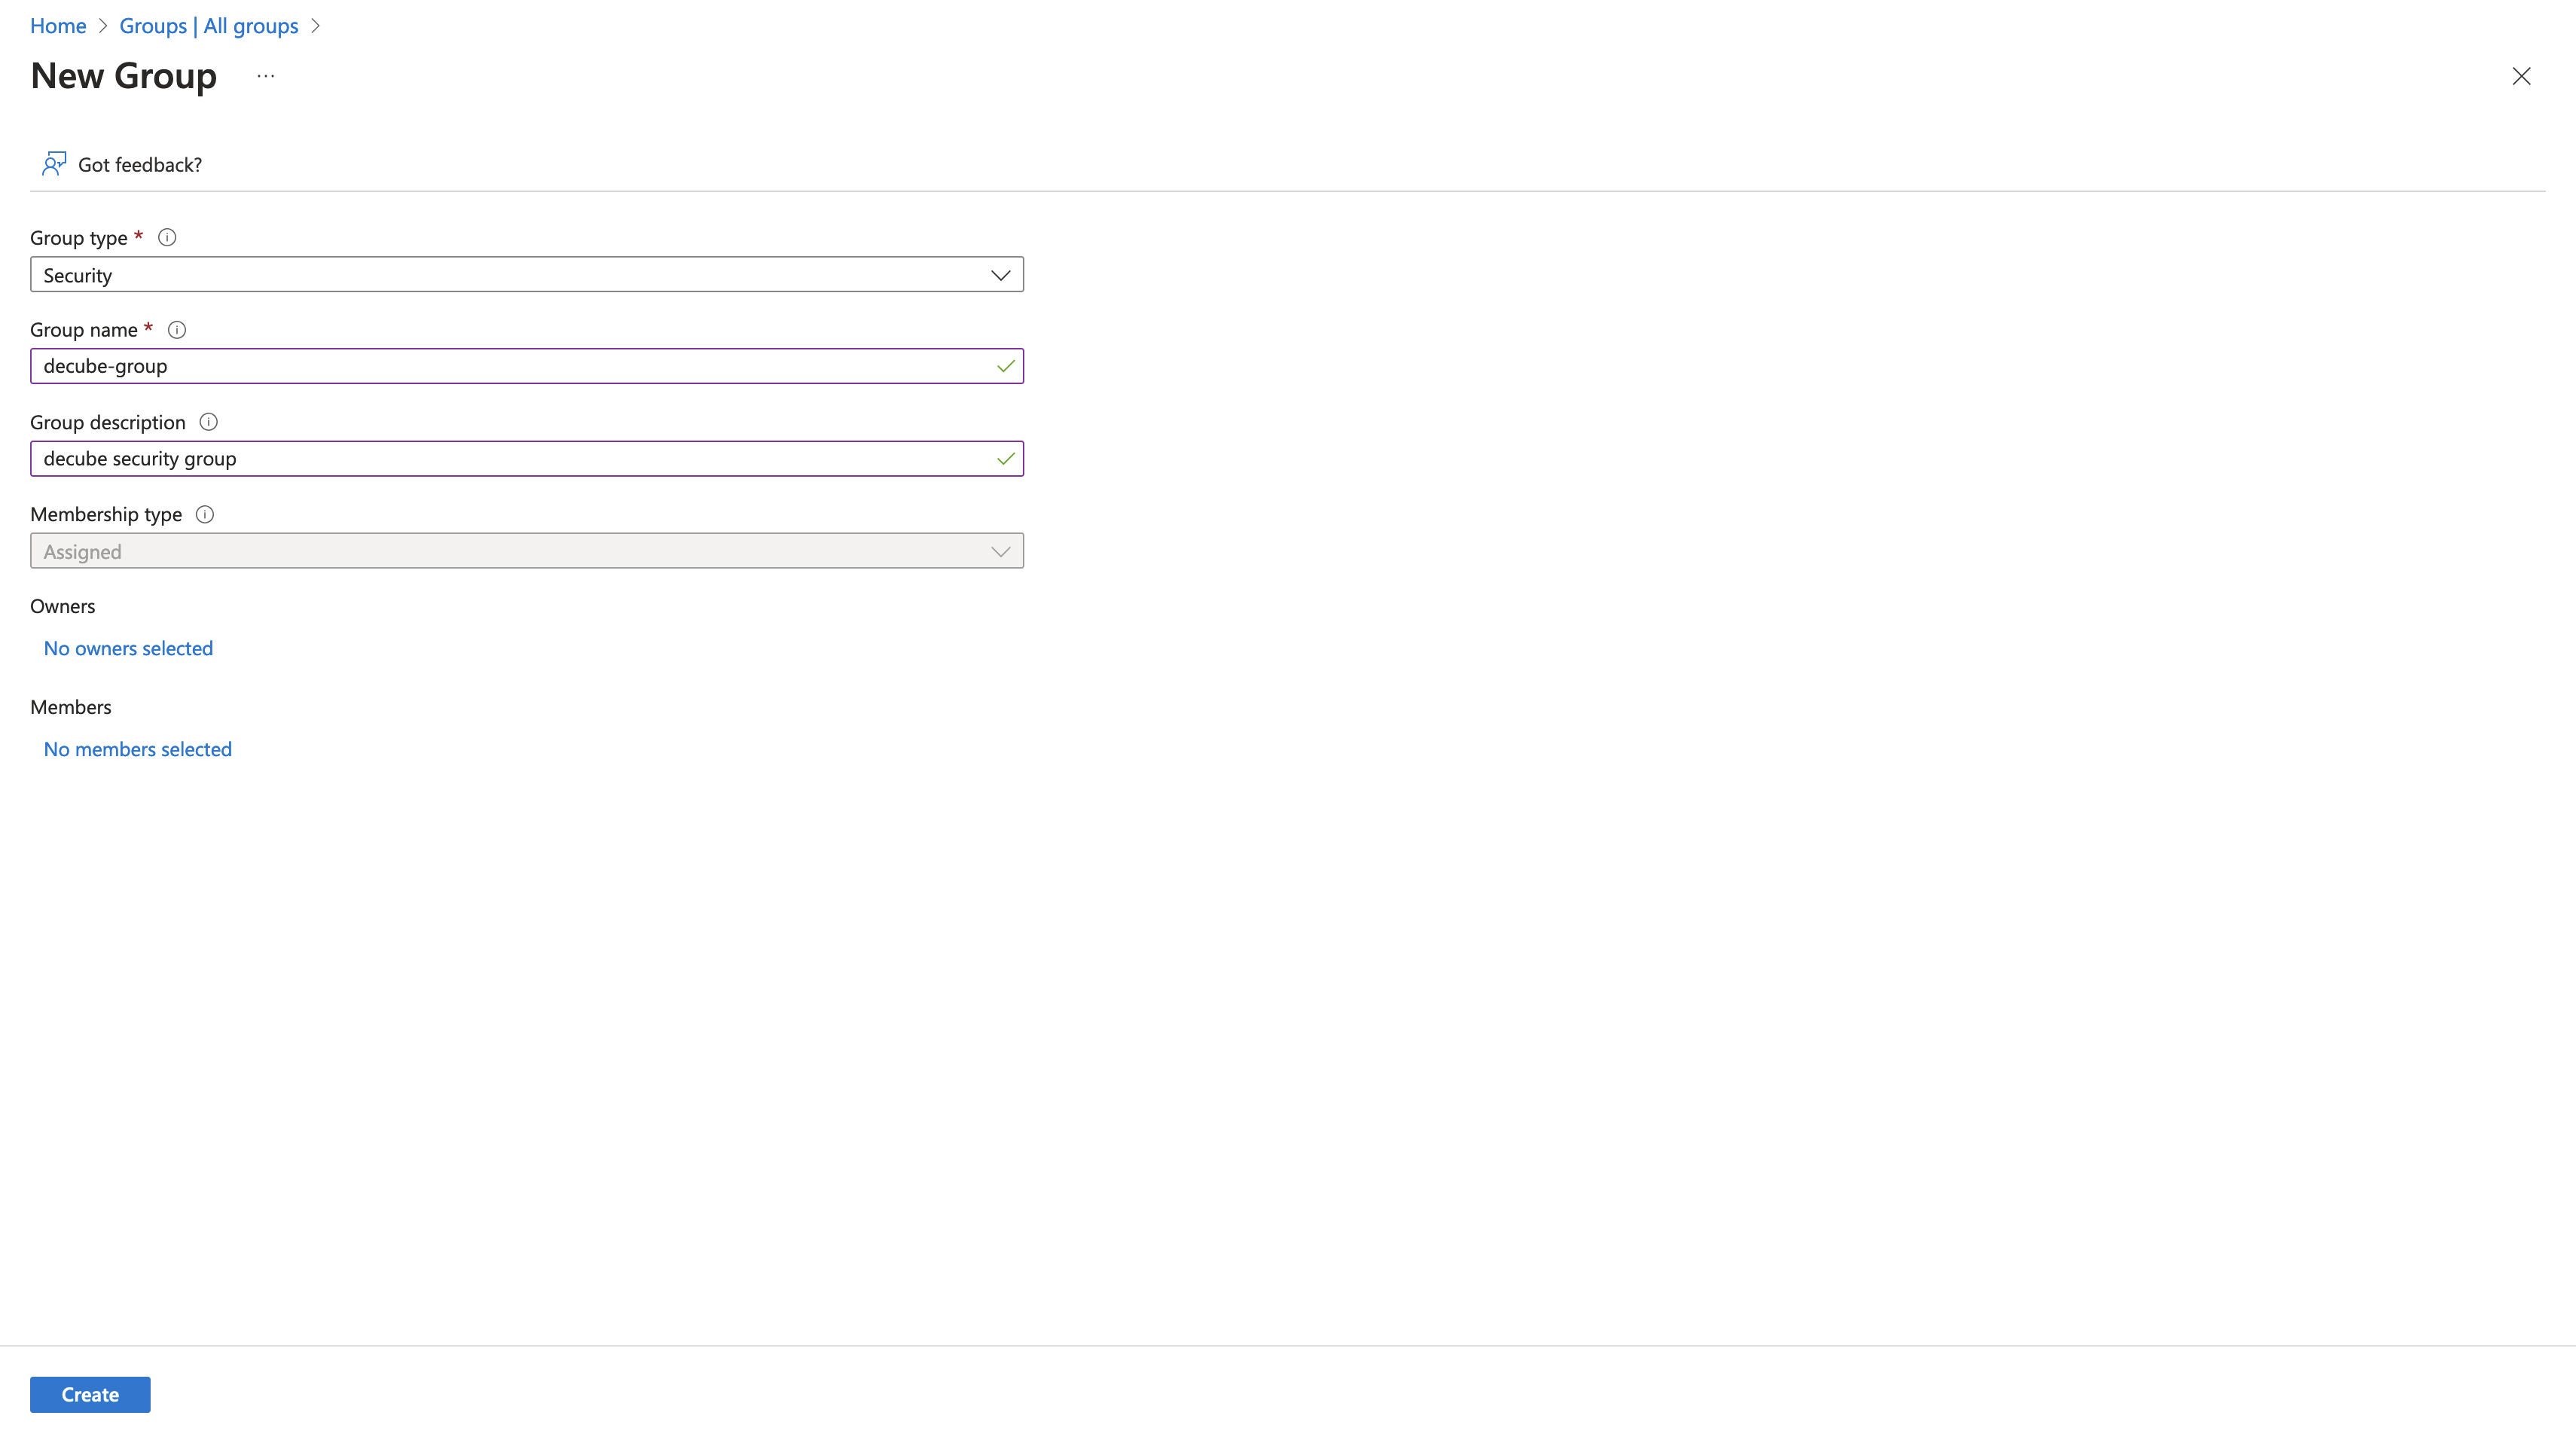
6. Go back to the Azure Active Directory main page and on the left tab again click on Groups. Click `Create New Group`.
7. Ensure Group Type is `Security.`
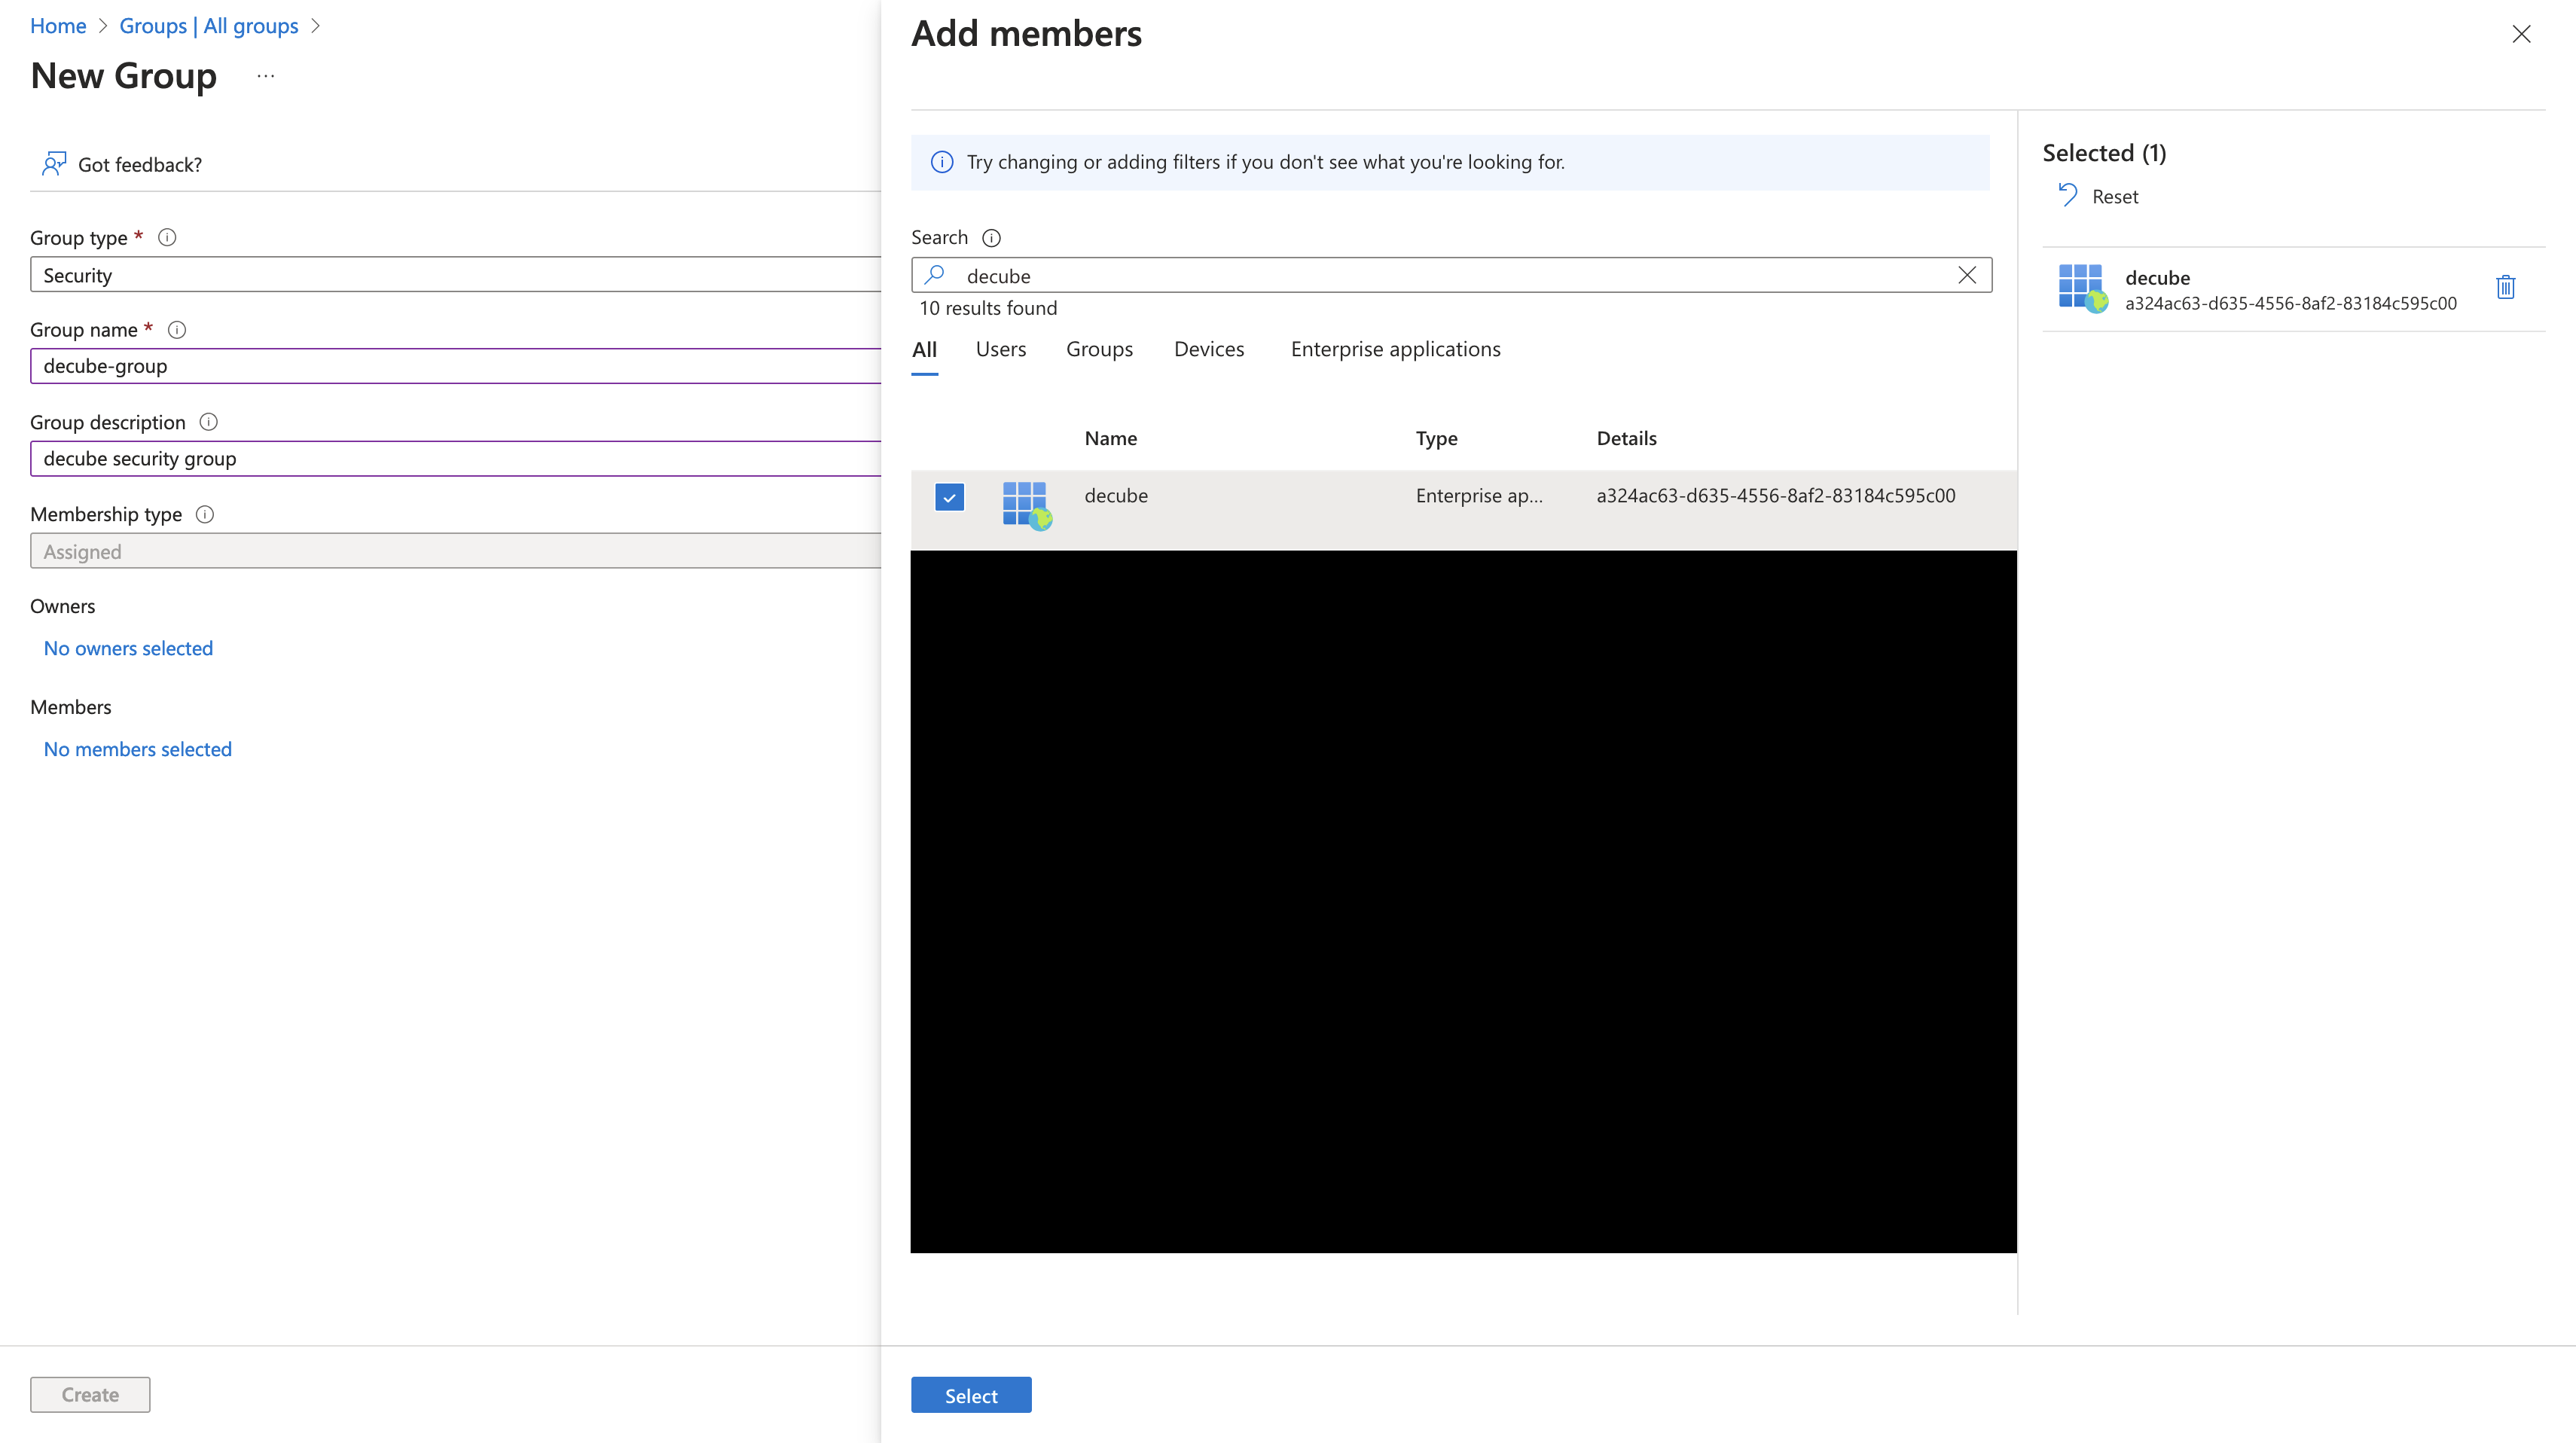
8. Click on members and search for the previously configured Service Principal. Here it would be `decube`.
9. Click on `Select` to add the service principal into the group.
10. Click on `Create` and we are done retrieving the `Tenant ID`, `Client ID` and `Client Secret` for this integration.
### Setting up and providing permissions to Service Principal
1. On the main PowerBI workspace page, on the top right corner, click on the gear icon to Setting and below `Governance and Insight` you will find `Admin Portal`.
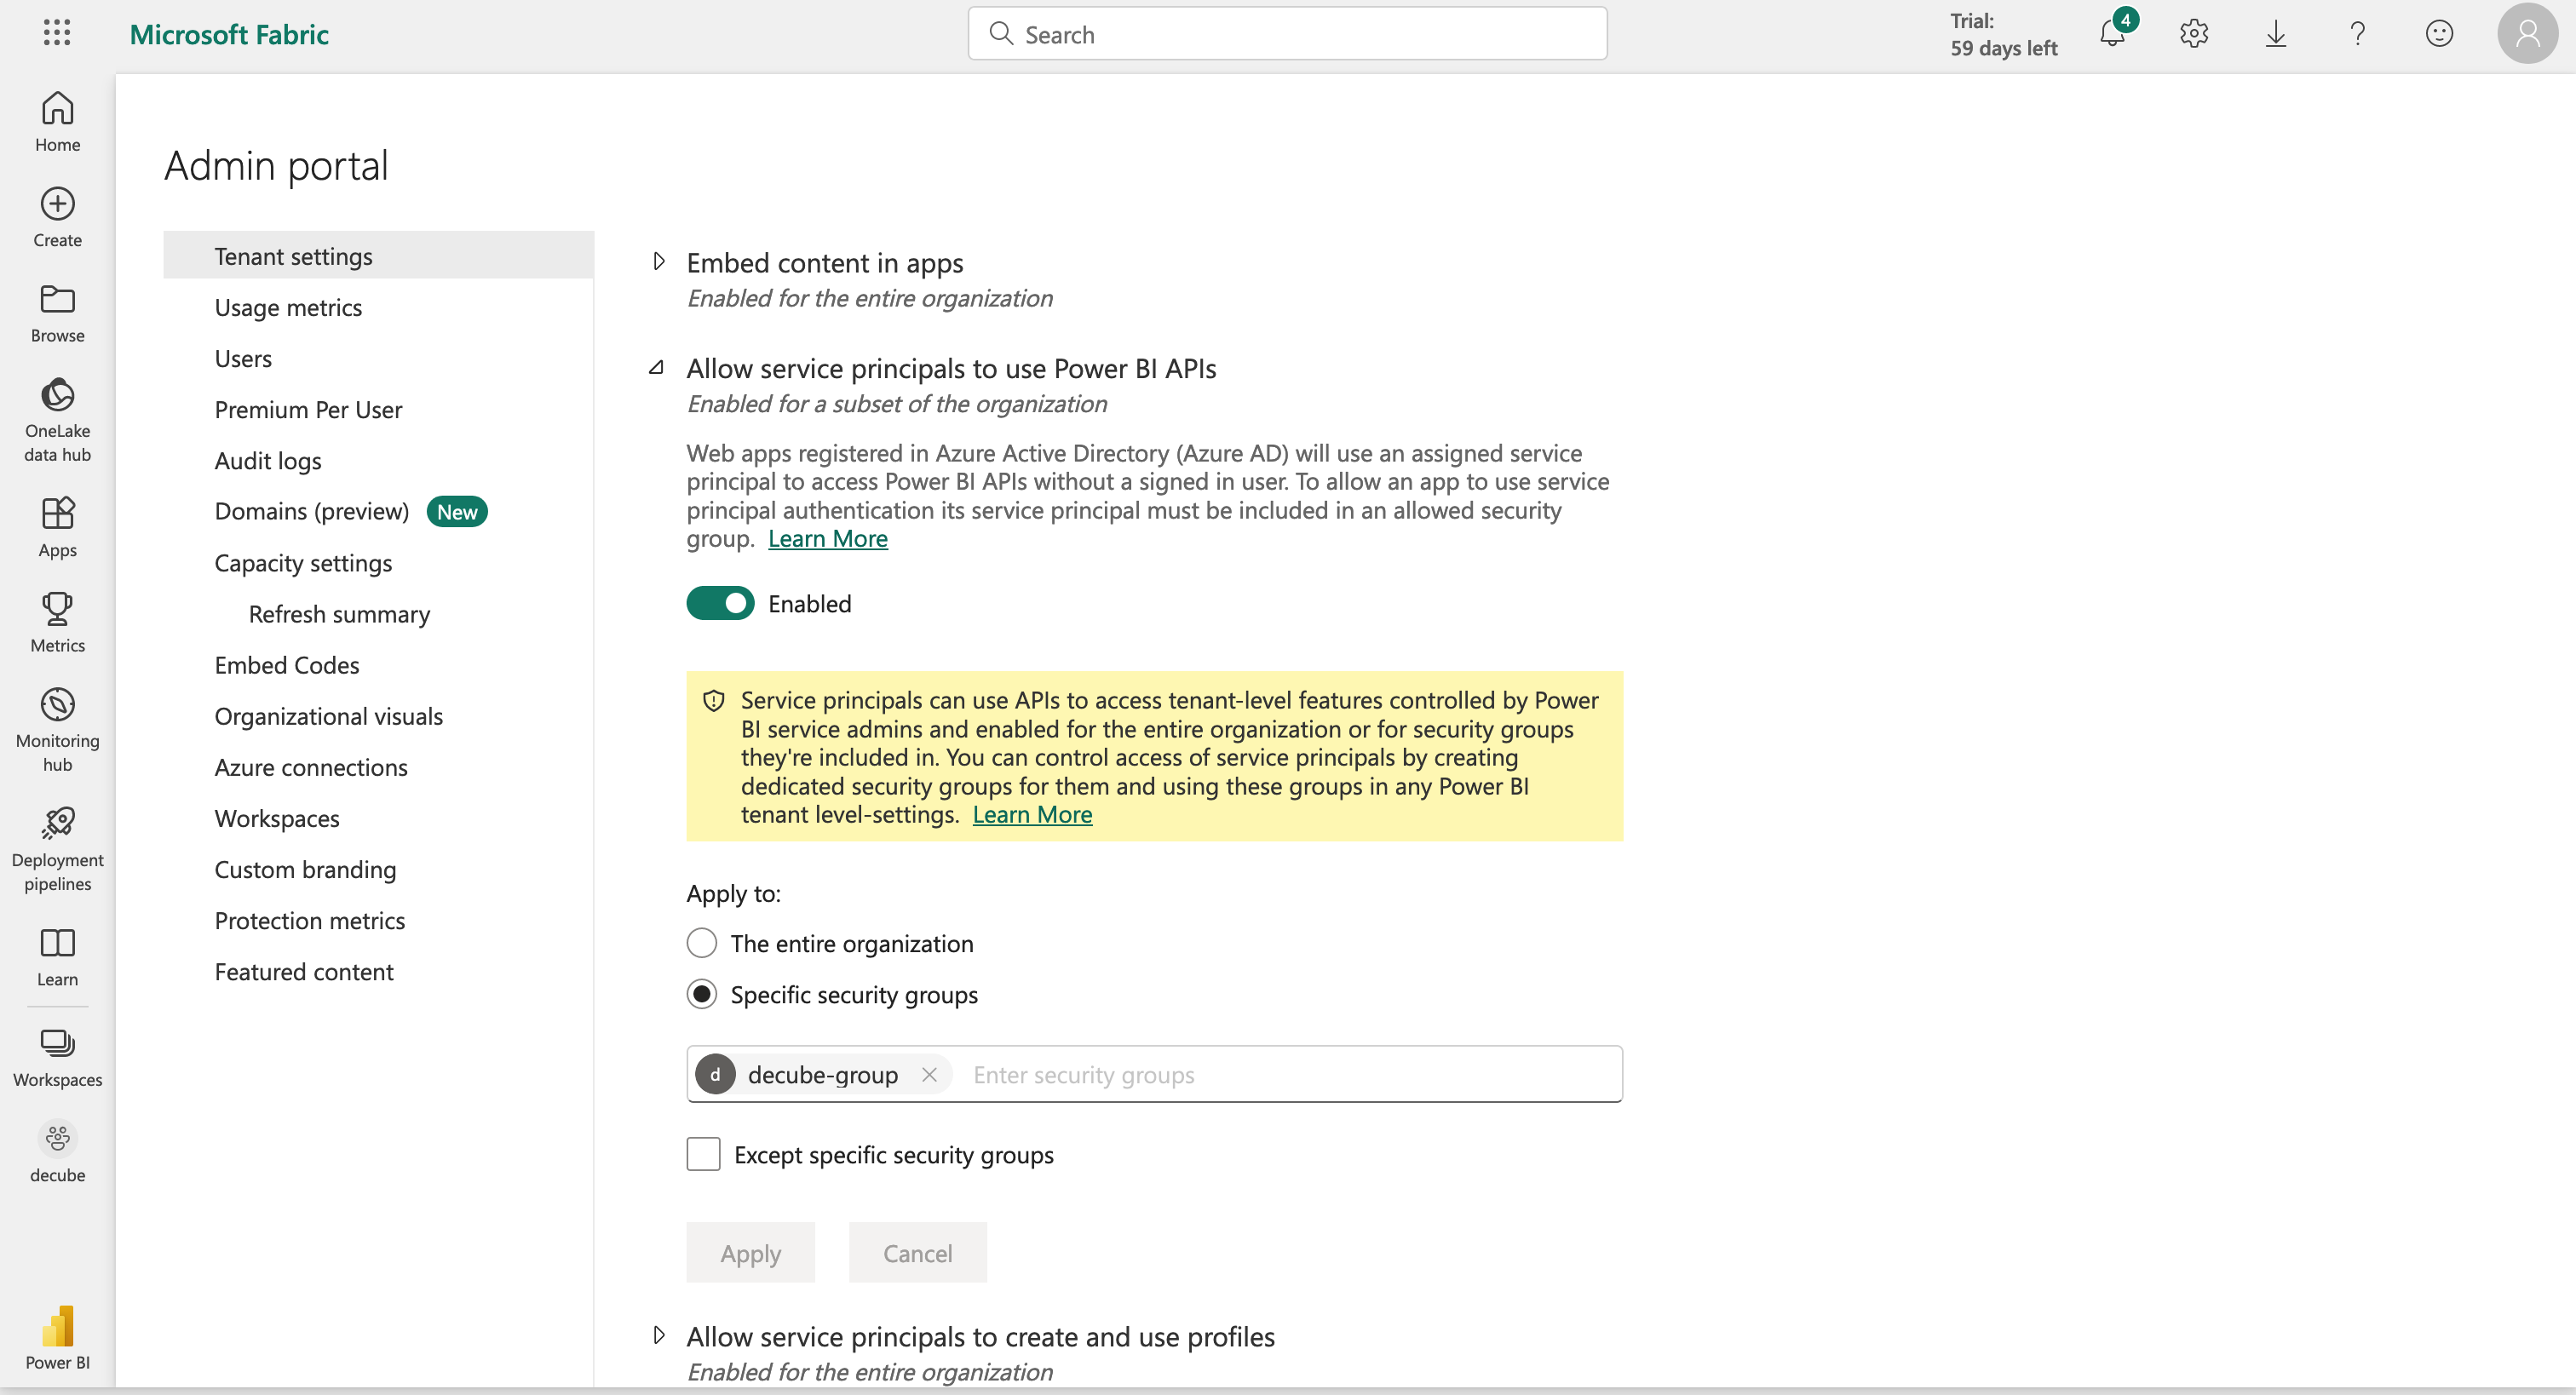
2. Here in the Admin Portal, find Tenant Settings and search for `Allow service principals to use Power BI APIs under Developer Settings`.
3. Enable it and either `Apply to Entire Organisation` or `Specific Security Group.` Here you can search for the one we created earlier. Example of how it should look like below.
4. Please enable and do this for the following settings as well under `Admin API` settings.
* `Allow service principals to use read-only admin APIs`
* `Enhance admin APIs responses with detailed metadata`
* `Enhance admin APIs responses with DAX and mashup expressions`
### Additional Configuration for lineage
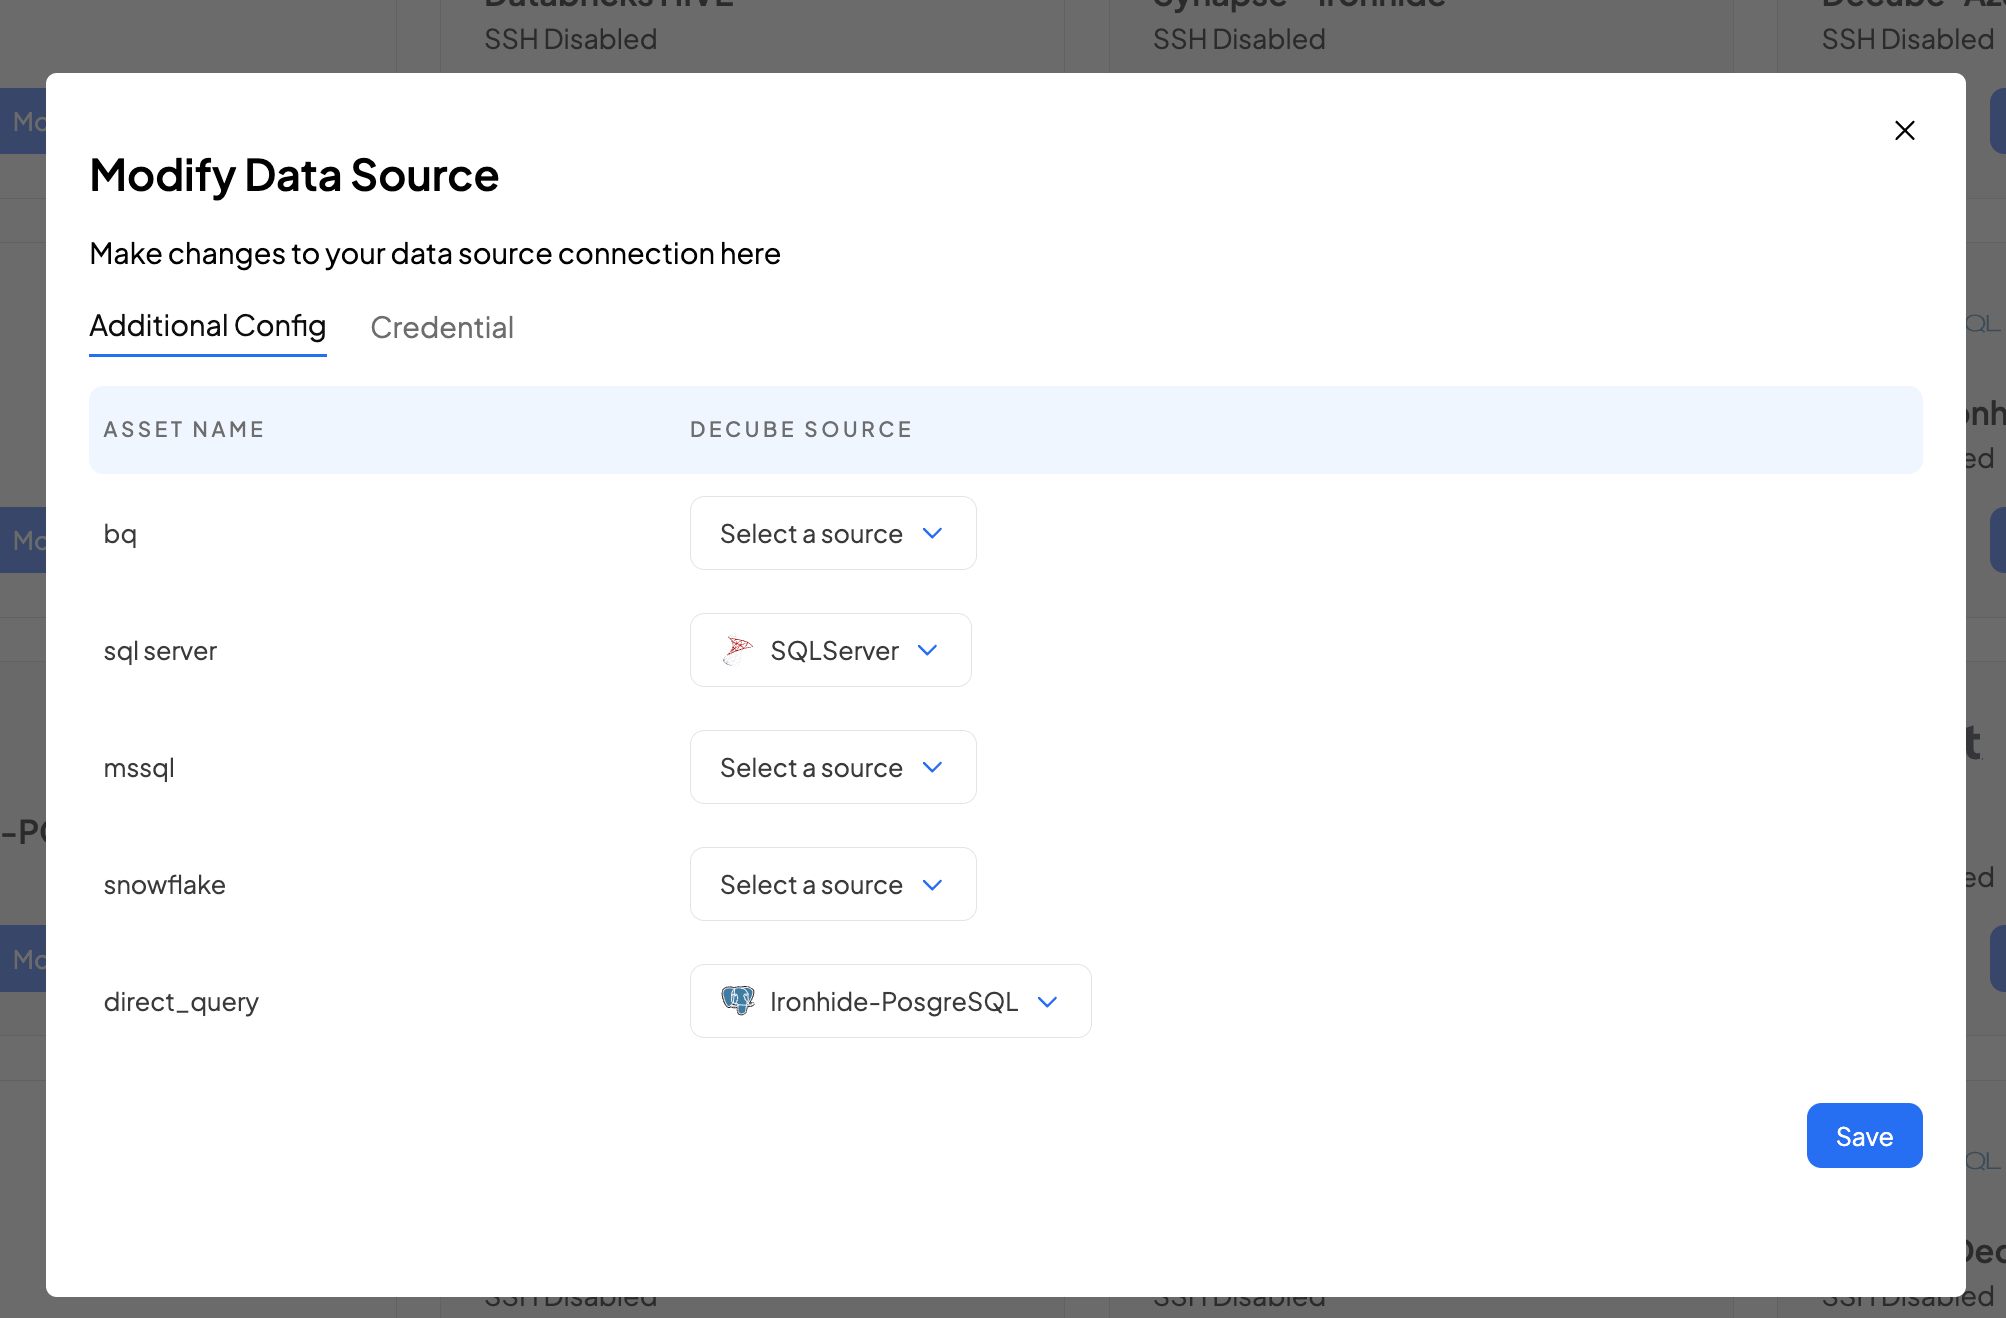
To build out the lineage, we will need to know the data sources that you've referenced within your PowerBI definitions. You can do a one-time mapping for the sources by going to the Data Sources page > Modify Data Source > Additional Config.